
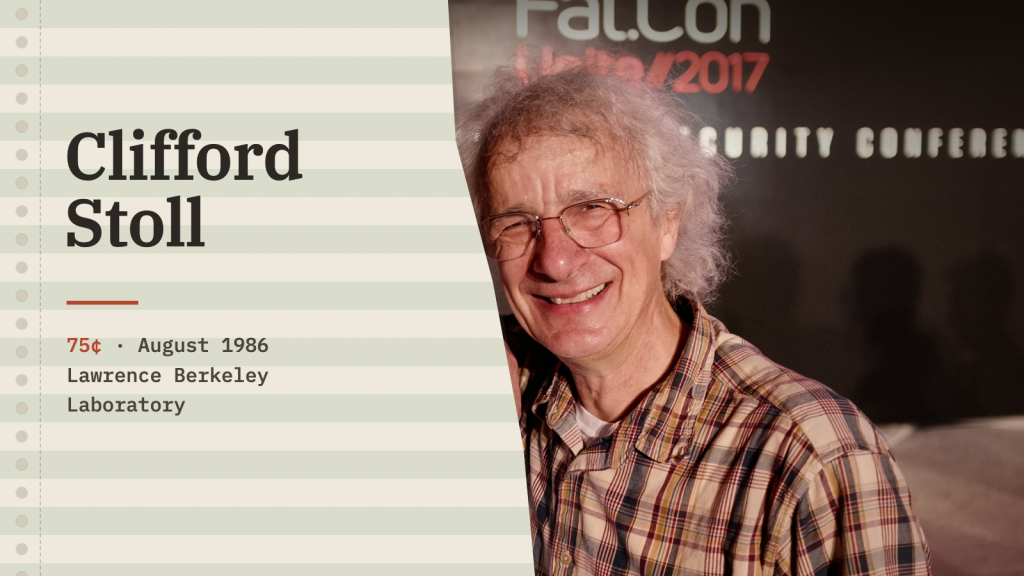
In August 1986, an accounting program at Lawrence Berkeley Laboratory (LBL) in California would not balance. The gap was 75 cents. Clifford Stoll, an astronomer who had switched to helping run the lab’s computers when his grant ran low, went looking for the cause. The trail led to a hacker in West Germany whose associates sold some of what he collected to the KGB, the Soviet intelligence service.
The 75 cents came from an account named “Hunter” that had no valid billing address. Soon afterwards, the US National Computer Security Center reported that someone at LBL had tried to break into one of its computers over MILNET, the US military’s data network. Stoll’s team deleted the stray account, but the problem remained: someone was acting as a system manager and trying to change the accounting records.
LBL did not slam the door. “Instead of trying to keep the intruder out, we took the novel approach of allowing him access while we printed out his activities and traced him to his source,” Stoll wrote in 1988. The trace took nearly a year.
How LBL watched the intruder without being seen
Stoll’s team put line printers and recorders on every incoming port and printed the traffic. Within a few days the intruder came back, and every keystroke landed on paper. The monitors sat outside the computers: a serial line can feed more than one device, so the printers copied the traffic without touching the operating system. Even an intruder with system-manager rights could not see them.
A monitor inside the system, Stoll noted, would have used resources, needed privileged software that could open new holes, and warned the intruder that he was being tracked. Within seconds of each connection, automatic alarms paged system managers and network control centers through a local modem, and technicians started tracing the call.
The hole was in a text editor
The printouts showed how he became system manager. GNU Emacs, a popular text editor, came with its own mail system. Its movemail facility used the Unix set-user-ID (setuid) feature, so part of the program ran with system-manager (root) privileges. Movemail let a user change who owned a file and move files into another user’s directory, but it did not stop anyone from moving a file into the system’s own area.
The intruder wrote a shell script that would grant him system privileges when it ran as root. He used movemail to slip the script into the system’s own area, disguised as a utility the system ran on a schedule. According to The Wall Street Journal’s 1989 account, that utility was atrun, which ran every five minutes. When the system ran his script, he gained system-manager privileges. Stoll’s 1989 book about the chase is titled The Cuckoo’s Egg: a cuckoo lays its egg in another bird’s nest and leaves the host to hatch it.
The wrong guess, and the clues that pointed abroad
At first, the lab suspected a student prankster from the nearby University of California. The evidence kept pointing elsewhere. Network round-trip delays suggested an overseas origin. The intruder used AT&T’s Unix commands rather than Berkeley’s, and when he stole accounts he sometimes chose German passwords. “In retrospect, all were clues to his origin,” Stoll wrote, “yet each was baffling given our mind-set that ‘it must be some student from the Berkeley campus.’”
Tymnet, a commercial data network, captured the calling addresses within seconds of each attack. The addresses pointed to universities in Bremen and Karlsruhe and to a public dial-up modem in another German city.
LBL itself was mostly a stepping stone into MILNET, the military network. From there the intruder tried to log in to about 450 computers with common account names such as root, guest, system and field. On about 5 percent of the machines he tried, default account names and passwords let him in. He searched files for words like “nuclear,” “sdi” and “norad,” the last two short for the Strategic Defense Initiative and the North American Aerospace Defense Command. In all, over 10 months, Stoll’s team watched him get into more than 30 computers.
The fake memos that finished the trace
Telephone technicians could narrow the calls down to a German city, but to reach a single telephone they needed a longer connection than his usual few minutes. According to a 1989 review of Stoll’s book, the ruse that kept him on the line was thought up by Martha Matthews, a Berkeley law student who later married Stoll. The lab created files of invented memos about how computers would support research for SDI, the US missile-defense program. The files also held a mailing list and form letters from an LBL secretary who did not exist.
The intruder found the files and spent more than an hour reading them. During that time, the technicians completed the trace. The lab celebrated with milkshakes made with homegrown Berkeley strawberries, but the celebration proved premature. A few months later, a letter arrived from someone in the United States, addressed to the nonexistent secretary and asking to be added to the fake SDI mailing list. Because it asked for “classified information,” Stoll wrote, the letter alone suggested espionage.
What the German court found
In March 1989, West German authorities arrested members of the group, including the intruder, Markus Hess of Hanover. Prosecutors charged three men: Hess, a second computer specialist, and a former croupier said to be the group’s contact with the KGB. According to The Wall Street Journal, Hess probably never reached top-secret files, but the KGB in East Berlin was willing to pay two of his associates for some of his material.
In early 1990, the Higher Regional Court in Celle gave all three suspended sentences: two years for the former croupier, 20 months for Hess and 14 months for the other specialist. The presiding judge, Leopold Spiller, said there could not have been much of value in the deliveries to the KGB agent in East Berlin.
What the short version of the story leaves out
In Stoll’s own short version, a 75-cent accounting error led him to a hacker who, “a year later,” turned out to be “a spy working for the Soviet KGB.” The real timeline was longer. The 75 cents only opened the case. Finishing the trace took nearly a year of printouts, phone traces in two countries and fake memos, and the charges of spying for the KGB came only in 1989.
Stoll also questioned the idea that breaking in takes brilliance. His paper calls the intruder “patient and plodding,” a man who “hardly showed creative brilliance in discovering new security flaws.” He reused documented holes, default passwords, and passwords that users had left in files and saved email.
What developers can take from the chase
- Reconciliation is monitoring. An accounting program that would not balance raised the first alarm.
- Monitors outside the system stay hidden. Printers on split serial lines were invisible even to root.
- Privileged helpers are attack surface. One setuid mail utility turned a user account into root.
- Default passwords are open doors. They let him into about 5 percent of the machines he tried.
The intruder needed no new tricks, only old holes. The defense needed no new tools either: paper, pagers and someone who would not let 75 cents go. Once warned, the other sites he attacked usually locked him out immediately, while LBL kept watching. As Stoll’s 1988 paper put it, “From the intruder’s viewpoint, almost everyone except LBL detected his activity. In reality, almost nobody except LBL detected him.”
Related stories
Sources
- Clifford Stoll, “Stalking the Wily Hacker,” Communications of the ACM 31(5), May 1988 (National Security Archive copy)
- George Melloan, “Who’s Spying on Our Computers?”, The Wall Street Journal, November 1, 1989 (text in a University of Pittsburgh research corpus)
- Simson L. Garfinkel, review of Clifford Stoll’s The Cuckoo’s Egg, The Christian Science Monitor, October 13, 1989
- “3 W. German hackers face charges of spying for KGB,” Deseret News, August 17, 1989
- “Urteil in Celle: KGB-Hacker bekamen eine Bewährungsstrafe,” Computerwoche, March 2, 1990 (German)
- Clifford Stoll, “Stalking the Wily Hacker,” talk abstract, SecretCon
- Featured image: Clifford Stoll at CrowdStrike Fal.Con in San Diego, “San Diego, California, USA – 53946478090” by heipei, via Wikimedia Commons, CC BY-SA 2.0
 SIGNAL TITANS

Leave a Reply