
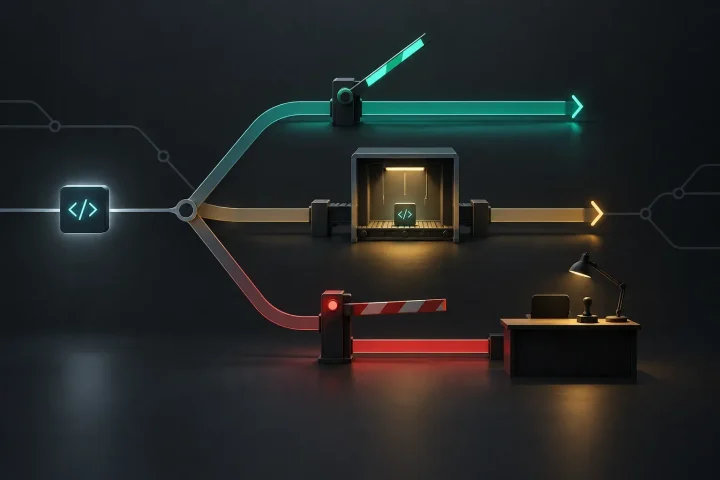
AI-generated editorial illustration; not a documentary photograph.
Anthropic’s AI-Native SDLC Playbook argues that AI agents are moving software development’s main constraint away from implementation and toward planning, review, verification, deployment and governance. A related analysis in The New Stack says the playbook and similar tools need to account for the different risks carried by different changes.
A wave of spec-driven tools
The playbook is part of a broader group of spec-driven development tools that includes Amazon’s Kiro and GitHub’s Spec Kit. These systems use version-controlled artifacts to connect intent, specifications, plans, code changes and review findings. They also emphasize deterministic enforcement mechanisms and agent self-checks before human approval.
One repository, several paths
The analysis argues that a fixed workflow is a poor fit for real engineering organizations. A documentation change, dependency upgrade and payments-service schema migration may require different verification, approvers and audit records. In regulated environments, the evidence and identities recorded during approval can also vary by change type.
When teams must force every change through the same sequence, they may bypass the tool for work that does not fit, making the organization’s actual process harder to see. Alternatively, configuration can grow until the tool becomes an opaque workflow engine.
Processes as rules
The proposed alternative models each process as a state machine made up of rules that react to facts in systems such as repositories, CI pipelines, clusters and issue trackers. A rule can require evidence, decide whether to act automatically or wait for approval, and grant a permission such as merging or deploying.
Under this model, processes do not track a fixed step number. They advance when relevant state appears, while gates can pause action during incidents or release freezes. The analysis says agent-reported results should not be sufficient evidence; tests and other systems outside the agent must provide it.
Routing by risk
The process assigned to a change should be determined by signals such as affected paths, repository location or issue labels, rather than by the author selecting a less demanding route. The source describes lighter handling for documentation fixes, compatibility evidence for dependency upgrades and additional domain review for payments-related schema migrations.
The analysis also treats process definitions as governed data: changing an approval rule should pass through its own review. It says autonomy can expand gradually for change classes as agents demonstrate reliability, while human attention remains focused on decisions requiring judgment.
Source: The AI-native SDLC won’t be one process
 SIGNAL TITANS
Leave a Reply